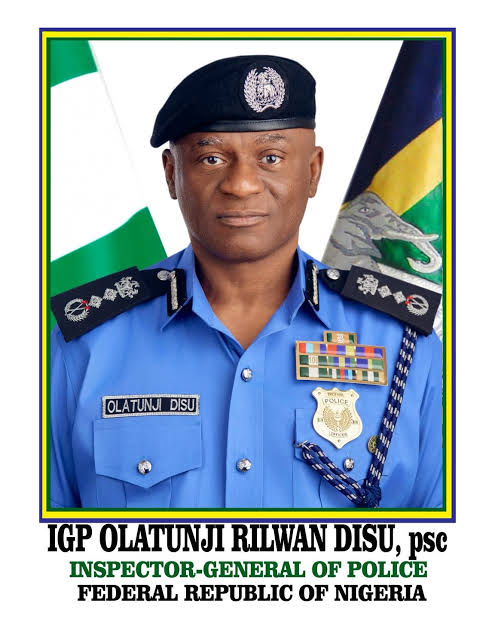
The Inspector-General of Police, Olatunji Rilwan Disu, has raised concerns over insider-enabled cybercrime in Nigeria’s financial sector, urging banks, fintech companies and payment service providers to strengthen internal controls and closely monitor employees’ access to sensitive systems.
Disu gave the warning on Thursday while declaring open the 2026 Cybersecurity Awareness Campaign of the Nigeria Police Force National Cybercrime Centre (NPF-NCCC) at the Nigeria Police Resource Centre, Jabi, Abuja.
The campaign, themed “Towards a Resilient Cyberspace: Think Before You Click,” aims to promote safer online practices, improve cybersecurity awareness and encourage collective action against digital crimes.
The IGP noted that Nigeria’s growing reliance on digital platforms for financial transactions, public services and everyday activities had increased exposure to online fraud, identity theft, data breaches, extortion and other cyber-enabled offences.
He stressed that protecting the country required safeguarding not only its physical territory but also the digital networks and systems that support businesses, institutions and individuals.
According to him, the police must adopt a proactive approach to cybersecurity by identifying warning signs, analysing emerging criminal methods and addressing vulnerabilities before threats escalate.
He said this would require intelligence-led policing, digital forensics, credible threat analysis, timely information sharing and stronger collaboration among relevant stakeholders.
Disu, however, emphasised that predictive policing must be guided by reliable intelligence, human oversight, the rule of law and respect for fundamental rights.
Describing personnel of the NPF-NCCC as the “Guardians of Nigeria’s Digital Frontier,” he charged the centre to strengthen its technical capacity to investigate cybercrime, preserve digital evidence, support victims and collaborate with relevant partners to dismantle criminal networks.
Addressing financial institutions, the police chief warned that cyber threats could originate from within organisations as well as from external attackers.
He identified possible insider threats as deliberate misconduct, collusion, compromised credentials, abuse of privileged access, negligence and weak supervision.
According to him, employees with legitimate access to sensitive systems, customer information and financial transactions could create opportunities for criminals that external attackers might find difficult to exploit.
He urged financial institutions to strengthen employee screening, access controls, separation of duties, transaction monitoring, internal audits, incident reporting and independent oversight.
The IGP also advised banks and fintech operators to closely regulate privileged access and investigate suspicious access patterns, unauthorised data extraction, irregular transaction approvals and unexplained account changes.
“This is not a judgment on the integrity of our workforce. It is a recognition that institutional trust must be reinforced by verification, accountability and disciplined controls,” he said.
Disu maintained that trust remained essential to the financial system but warned that trust without verification could become a vulnerability.
He assured financial institutions that the police, through the NPF-NCCC and in collaboration with regulators and other relevant agencies, would continue to support the lawful detection, investigation and disruption of cyber-enabled financial crimes, including offences involving insider collusion.
He added that investigations would be conducted professionally and impartially, in accordance with the law, whenever evidence indicated criminal conduct.
The IGP also called for a coordinated national response to cybercrime, involving government agencies, law enforcement institutions, regulators, financial institutions, technology providers, educational institutions, civil society organisations, the media and members of the public.
He urged stakeholders to strengthen threat-intelligence sharing, incident reporting, digital-evidence preservation and coordinated responses to emerging cyber threats.
Disu further called on Nigerians to adopt safer online habits by verifying links before clicking, confirming payment instructions through independent channels, protecting passwords and one-time passwords, enabling multi-factor authentication and keeping devices updated.
He warned that simple precautions could prevent significant financial and personal losses, urging citizens to verify information before sharing it and promptly report suspicious activities.
Addressing Nigerian youths, Disu urged them to channel their digital skills into legitimate careers and technological innovation rather than cybercrime.
He said skills that could be used for fraud, impersonation, harassment and exploitation could instead support careers in cybersecurity, software development and technology entrepreneurship.
The police chief warned young people against allowing the pursuit of quick money or the perceived glamour of online fraud to jeopardise their future.
“Choose creativity over criminality, integrity over shortcuts, and innovation over exploitation,” he urged.
He encouraged young people experiencing or witnessing online fraud, cyberbullying, sextortion, recruitment into cybercrime and other forms of digital abuse to seek assistance and report such incidents through appropriate channels.
Disu concluded that a resilient cyberspace was one in which risks were anticipated, vulnerabilities reduced, threats detected early and responses coordinated.
He urged stakeholders to translate the campaign’s message into safer online practices, stronger institutional controls and sustained cooperation.
Reiterating the campaign’s central message, the IGP urged Nigerians to “Think Before You Click. Verify Before You Share. Report Suspicious Activity.”
He subsequently declared the 2026 Cybersecurity Awareness Campaign of the NPF-NCCC open, expressing confidence that collective efforts would help build a safer and more resilient Nigerian cyberspace.